The news logged on this beat over the past week points to one thread: agent security is no longer a governance slide in someone else's deck. It is becoming developer tooling. Rig Security raised money to watch agents running under employee accounts, Komprise shipped a single interface for agents to reach enterprise data, and Okta turned its agent security framework into a multivendor reference architecture. Each of those products is aimed at a different layer of the same stack, and each one is asking the people who write code to make a decision.
The blind spot is where developers live
Rig Security's launch, as SiliconANGLE reported, came with $12 million in new funding and a specific observation about how identity activity gets recorded. Coding assistants and autonomous agents seldom sign in under their own credentials. They run under an employee's account, which means the activity looks like the employee did it. That is not an edge case; it is how most agent deployments begin, because it is the path of least resistance in any codebase that already has a working login.
The practical consequence for US development teams is that audit trails, permission reviews, and incident response all inherit a gap the moment an agent is wired into a repository, a ticketing system, or a cloud console. The product Rig is selling sits upstream of the code, but the fix lands in the code: agents need identity distinct from the human who launched them. That is a tooling change, not a policy memo.
One interface beats a sprawl of connectors
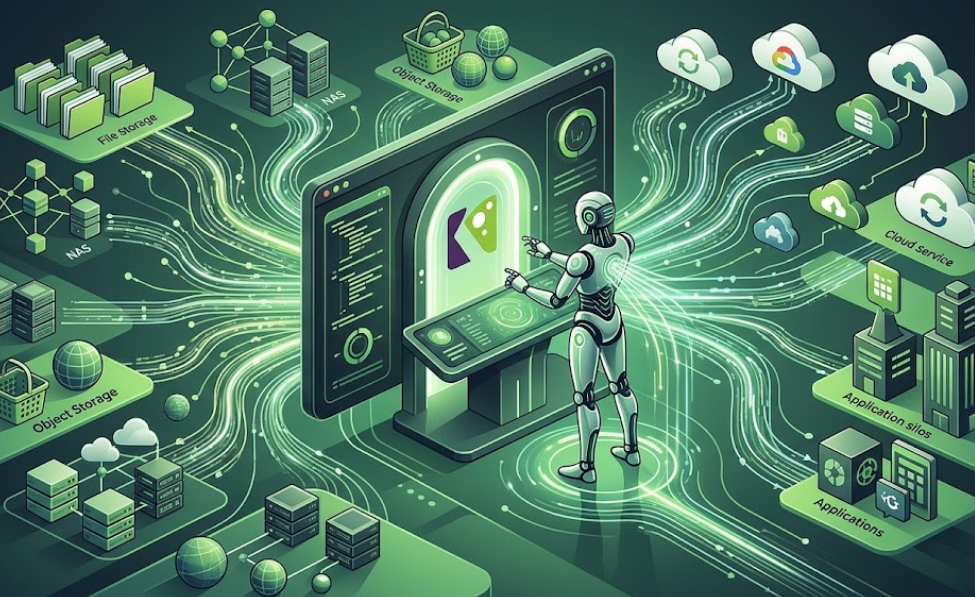
Komprise framed its launch as a response to what it calls MCP bloat. The open-source Model Context Protocol has become a common way for AI agents and large language models to reach third-party data, and the result is a growing pile of connectors, each with its own assumptions. Komprise's Universal File MCP tool, announced today and covered by SiliconANGLE, offers a single interface for querying any kind of data source.
For developers, the appeal is not elegance for its own sake. Every connector is code that must be written, tested, and maintained against a moving target. When a US enterprise wants an internal agent to answer questions across file shares, object storage, and the systems around them, the integration work is the project. A universal interface does not remove the security question, but it collapses the surface area where access controls get configured inconsistently. That is the same lesson the API gateway era taught, applied to a new class of client.
Runtime is where the frameworks meet the code
Okta's move, also reported by SiliconANGLE, is the clearest sign that this is settling into architecture rather than product marketing. The company turned its agent security framework into a multivendor reference architecture through the Blueprint Alliance, with the stated intent of helping buyers navigate competing vendor claims. Okta's president and chief operating officer, Eric Kelleher, is quoted in that coverage describing the effort in those terms.
Agent runtime security, as the story puts it, requires controls across the technology stack once enterprises move agents into production. That phrase matters on this beat because runtime is where developers actually work. A reference architecture that spans vendors is only useful if it maps to the points where code executes, where credentials are issued, and where data is fetched. If the blueprint stays at the level of procurement categories, developers will route around it. If it names concrete integration points, it becomes something a team can implement.

