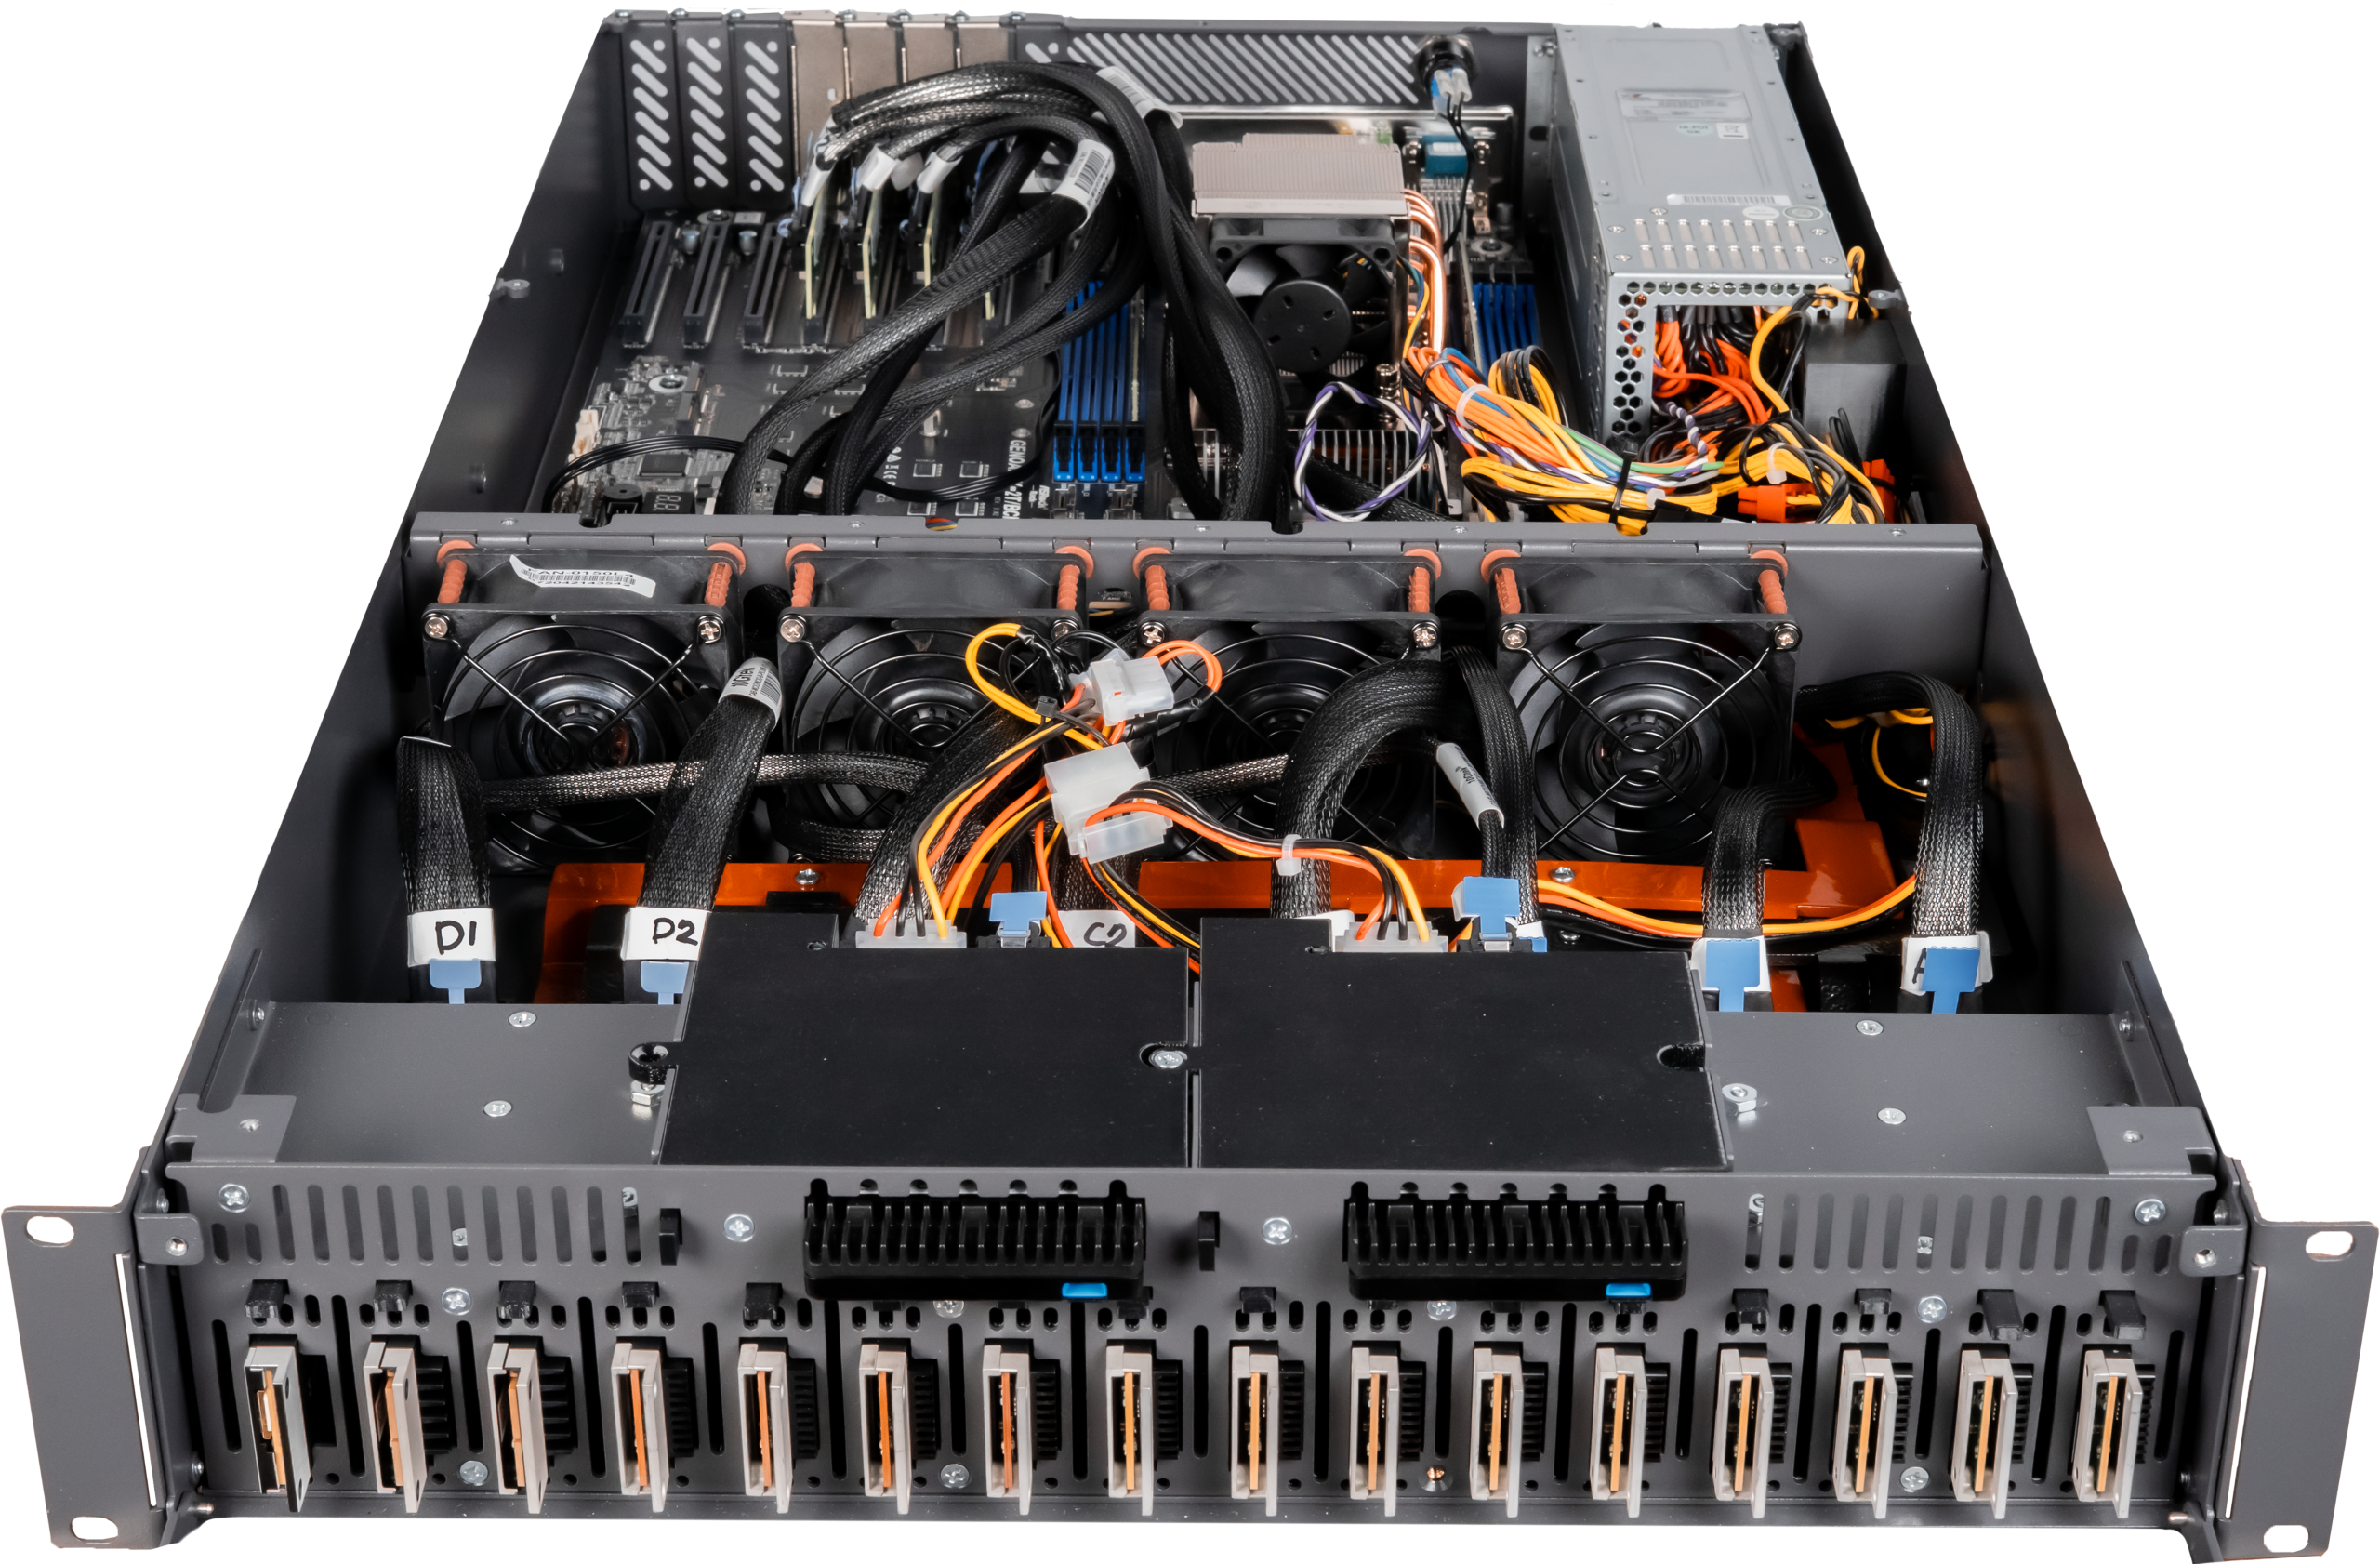
45Drives Ltd., the open-source data storage vendor, said today that its SnapShield cybersecurity platform now guards against data exfiltration and can be administered centrally across many servers and sites. SnapShield is marketed by the high-density storage maker as a final barrier against ransomware, blocking malicious payloads before they reach enterprise data. The software runs on the storage servers themselves, inspecting file activity for behavior that looks suspicious.
According to 45Drives, the platform can cut off a suspected user or client once activity crosses set thresholds, while other users and systems keep working. The company describes SnapShield as a complement to firewalls, endpoint security, network monitoring and backups, not a replacement for them. It requires no agent, so nothing has to be installed on individual workstations. Founder Douglas Milburn said storage servers are an excellent place to add a new layer of defense.
The newly added Data Exfiltration Protection feature pushes behavioral analysis past encryption to catch signs of data being taken out, which usually means repeated file reads followed by outbound movement. SnapShield looks for unusual patterns, including jumps in file access and contact with decoy honey files that appear sensitive. When activity exceeds a threshold, the platform can alert administrators or automatically isolate the user or IP address involved. It also includes Precision Restore, which pinpoints files touched during an attack so administrators can roll back only the damaged data instead of restoring a whole environment.
45Drives built SnapShield after it was hit by a ransomware attack that arrived through a socially engineered email. Backups were available, Milburn said, but finding the affected computers and deciding which files to restore was disruptive and slow. That experience pushed the company to seek a way to halt attacks nearer to their intended target. Milburn said activity across just a few files can trigger containment, which limits damage in environments holding hundreds of thousands or millions of files. The goal, he said, is containment: when something malicious slips past traditional defenses, the compromised system should be stopped from further damaging or reaching the data.
The platform supports Rocky Linux and Ubuntu deployments, covering single servers and multinode Ceph clusters installed with an Ansible playbook. Real-time email and system notifications are meant to keep administrators informed as suspicious events develop. Milburn acknowledged that legitimate activity can sometimes set off a false positive, and said administrators can briefly turn off protection for particular users or time windows when maintenance or another unusual task might look malicious.
The second major addition, the Centralized Management System, tackles the problem of running SnapShield one server or one cluster at a time. It offers a single console for viewing deployments, active events, user activity, analytics and audit logs, and lets administrators drill into an affected system. The feature targets large enterprises and managed service providers that oversee multiple sites or customer environments.
More cybersecurity news from TechManNews.