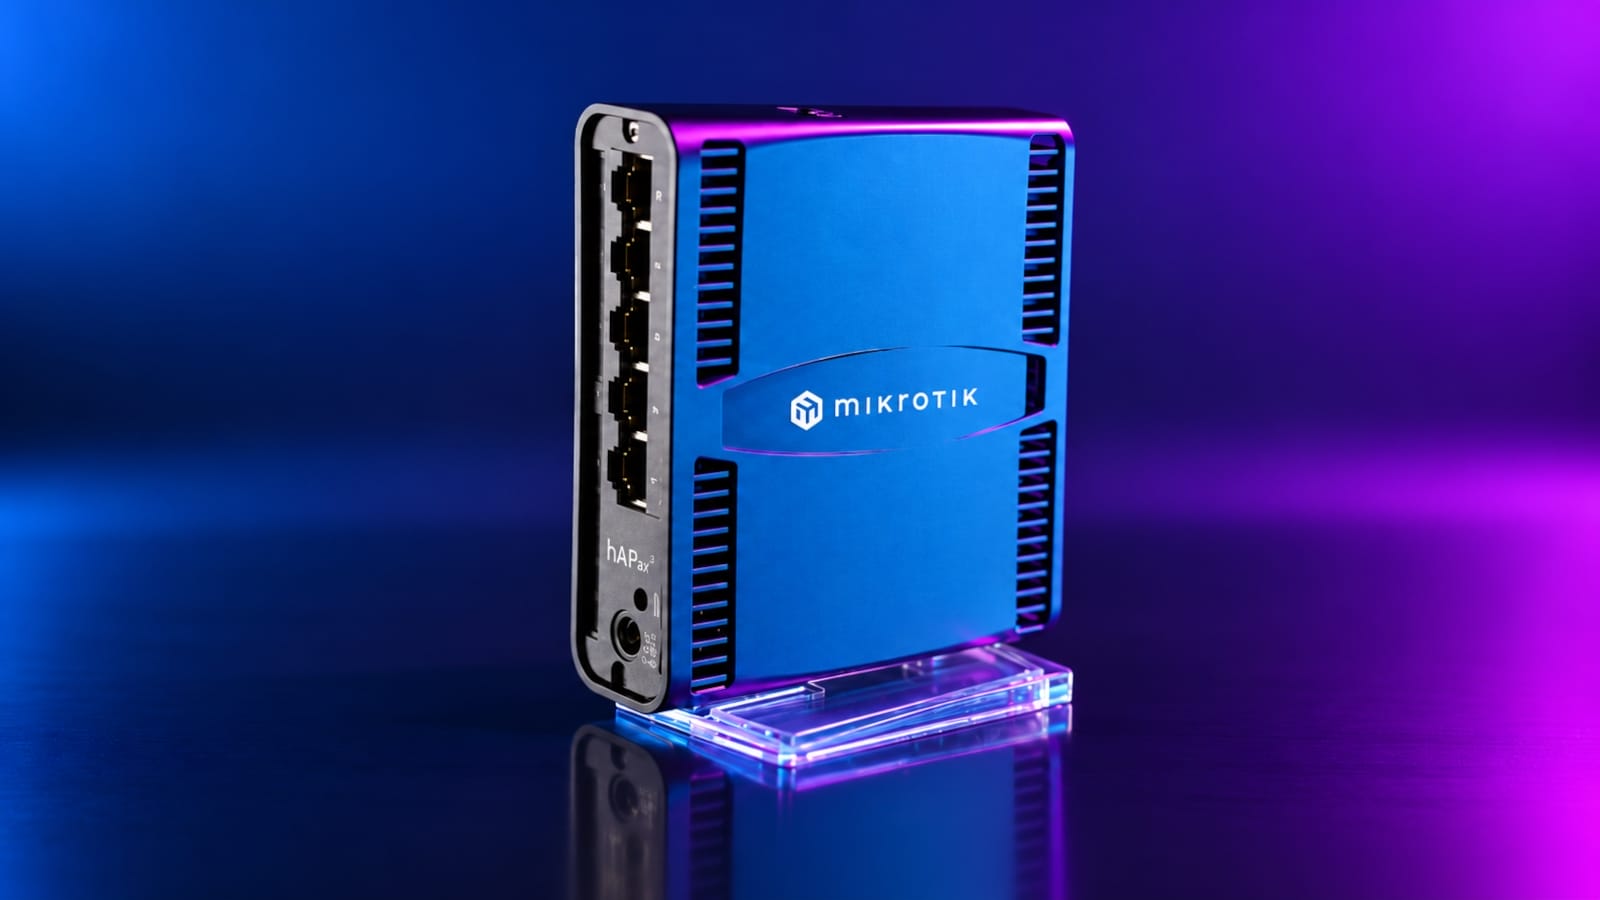
The U.S. Cybersecurity and Infrastructure Security Agency is alerting organizations to a critical flaw in MikroTik RouterOS that can be triggered before a user logs in. The vulnerability, tracked as CVE-2026-84411, is an integer underflow in how the router operating system handles HTTP request bodies through its web management service. CISA said a single crafted request is enough to let an unauthenticated attacker on the network run arbitrary code with root privileges or knock the device offline. The agency said it has no information indicating the flaw is being exploited in the wild.
According to CISA, the bug is reachable prior to authentication, which raises the risk for internet-facing routers. Because successful exploitation yields root-level code execution or a denial-of-service condition, affected devices could be fully controlled or taken down by an attacker who can send traffic to the web management service. CISA issued the advisory to make organizations aware of the exposure and to lay out defensive steps.
CISA said MikroTik RouterOS versions below 7.24 are affected. The agency also noted that the vendor recommends users move to version 7.23 or later to reduce the risk. Both the latest stable release, 7.24.4, and the most recent long-term release, 7.23.7, have been available since September 16. As of publication, MikroTik had not published a security advisory covering CVE-2026-84411.
The alert follows recent warnings about MikroTik devices as a target. Poland's CERT agency reported that attackers chained two RouterOS vulnerabilities, CVE-2026-67276 and CVE-2026-86060, to seize full control of devices with SSH services exposed to the internet. That campaign illustrates the interest attackers and botnet malware have shown in MikroTik flaws.
CISA's advisory includes recommended defensive actions for owners of MikroTik routers. The agency has not disclosed any public evidence of active exploitation of CVE-2026-84411. Questions sent to MikroTik and CISA about which RouterOS versions are affected had not drawn a response as of publication.
More cybersecurity news from TechManNews.