Vulnerabilities
52 stories · back to Cybersecurity
CISA orders feds to patch exploited Citrix flaws by Wednesday
The Cybersecurity and Infrastructure Security Agency (CISA) has ordered U.S. government agencies over the weekend to secure their systems against attacks exploiting two critical Citrix NetScaler vulnerabilities.

Citrix admins warned to shut down NetScalers over 2 exploited zero-days
Two unpatched Citrix NetScaler zero-day vulnerabilities are reportedly being exploited in attacks, with cybersecurity agencies, security researchers, and IT providers privately warning organizations about the flaws ahead of patches expected next week.
Cloudflare fixes Containers cross-tenant flaw exposing customer data
Cloudflare has fixed a vulnerability in Containers and Sandboxes that allowed customers with a Workers Paid account to recover residual data from other customers' containers on the same physical host.
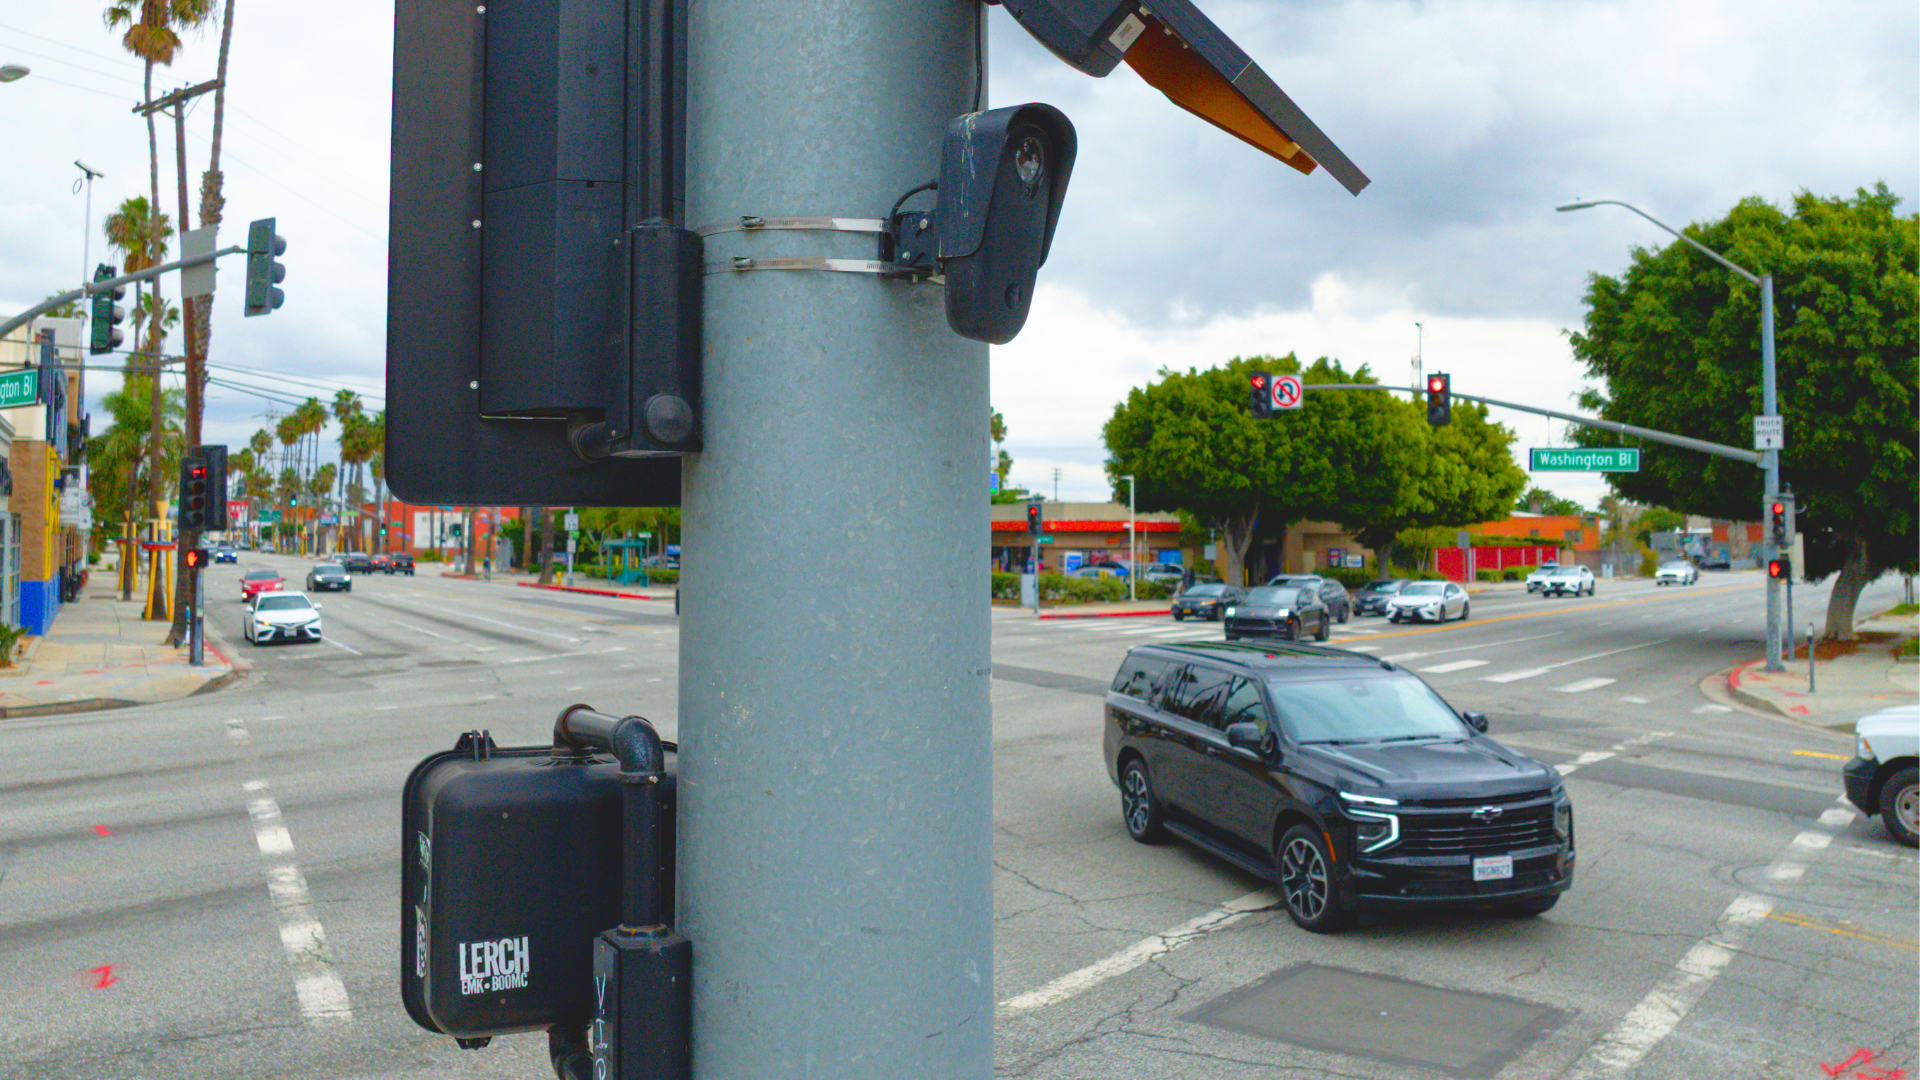
Flock seeks to have security researchers' map of Flock cameras taken down
A vulnerability on the Flock website allowed a security researcher to access its third-party provider to download the locations and descriptions of over 300,000 Flock cameras.

ShinyHunters uses WAF bypass trick in Oracle PeopleSoft attacks
The ShinyHunters extortion gang is using a URL-encoding trick to bypass web application firewall rules that mitigate the Oracle PeopleSoft CVE-2026-35273 flaw, allowing the threat actors to resume widespread exploitation of a flaw on vulnerable servers.

ShinyHunters hacked Clop leak site using Grav CMS path traversal flaw
The Clop ransomware gang has moved its data leak site to a new Tor address after confirming its previous server was compromised and defaced through an unpatched Grav CMS flaw that BleepingComputer has learned is an unauthenticated path traversal vulnerability.
CISA warns of Sharepoint, WSO2, Adobe Commerce flaws exploited in attacks
The Cybersecurity and Infrastructure Security Agency (CISA) warns that hackers are exploiting a critical authentication bypass vulnerability (CVE-2026-5430) affecting multiple products from enterprise software provider WSO2.
OpenAI hacked Australian Medicare govt site, probed data providers
OpenAI agents targeted public data providers in multiple countries, probing some for vulnerabilities and exploiting a security weakness in an Australian government portal while performing information-retrieval tasks as part of a research project.

How to fix your Windows File History if the September update broke it
A bug in the Windows Sept patch Tuesday update may stop File History from working. But a new optional update fixes it.

Meta’s Muse AI Assistant Rolled Out With a Serious Security Flaw
Meta says it issued a fix for the Muse zero-day vulnerability that would have let attackers do “whatever” they wanted on a victim’s Mac, highlighting the inherent dangers of AI helpers.
Our Latest Articles

Unpatched Flaws Are the Common Thread in Three New Exploits
12 hours agoDefender Zero-Day and CISA Alerts Expose an Unpatched US Attack Surface
1 day agoThe Vulnerability Is Now the Business Relationship
2 days ago
AI Is Both Weapon and Target in the Vulnerability Explosion
3 days ago