Cryptomining malware that conceals the location of its command-and-control server inside a GitHub poem has infected more than 3,400 servers, according to research from Lumen. The payload pairs the XMRig and Iron miners with Kryptex mining infrastructure, and compromised machines are turned into scanners and exploit servers. The campaign's first 900 victims shared one notable trait, Lumen found: contact with an endpoint belonging to the Russian crypto mining service. That pattern points to a financial motive.
The attackers concentrated on several widely used services. LiteLLM, a proxy that lets companies route applications to many large language models through a single endpoint, was a primary target, along with Gotenberg, a Docker-based PDF conversion API whose documentation warns against exposing it to the internet. Ollama, which runs open-weight models on local hardware and is not internet-exposed by default, and Gitea, a self-hosted Git platform, were also hit. Ivanti Sentry, an enterprise gateway appliance, may have been targeted as well, and a single instance of that product is how Lumen first found the campaign.
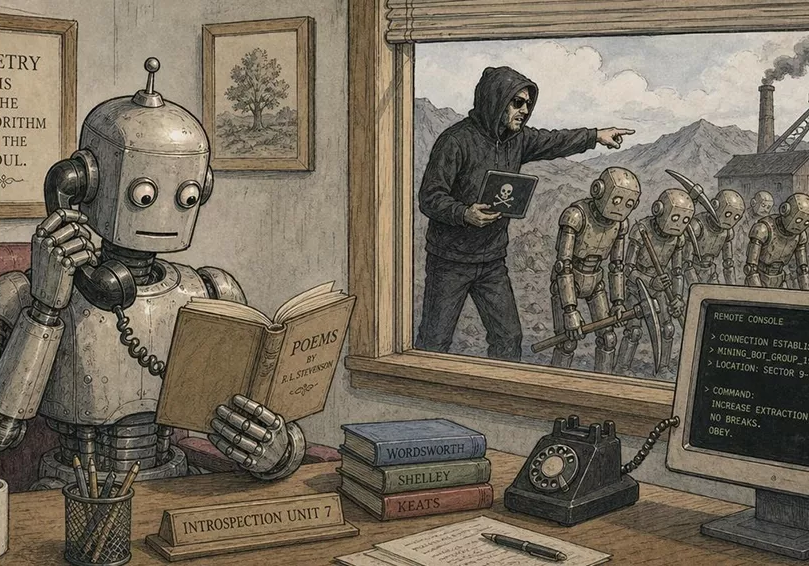
The poem itself, titled "On the Nature of Connection," first appeared in April, and each new version points to a different C2 server. The malware decodes the current address by pulling specific words from the text and converting them into an IPv4 address. Lumen said the creator had not altered the deciphering pattern at the time of its reporting. Researchers told The Register that a poem works well for obfuscation because it is an effective way to hide an important message. Lumen said this technique is unrelated to AI jailbreaking through harmful requests or prompt injection, sometimes described as adversarial poetry.
Infection came through exploitation of vulnerabilities in publicly exposed services, with broad scanning underway by May. For LiteLLM, a crafted POST to the connection endpoint was the likely path, based on a flaw that let two endpoints run a supplied command on the host without a role check, tracked as CVE-2026-42271, which CISA added to its exploited vulnerabilities list in June. Lumen did not detail how Ollama, Gotenberg, or Gitea were breached. The firm said exposed AI services are attractive targets because they can hold valuable data and hardware access, particularly GPUs.
Lumen said it has blocked all traffic to and from the PoeLLM C2 servers. At the time its report was published, three of 12 C2 servers remained active and the campaign was still infecting new victims, with the firm saying it would keep monitoring for new traffic. It also said enterprise attack surfaces are expanding rapidly as AI infrastructure grows. Administrators can check connection logs against indicators of compromise listed on Lumen's GitHub page, audit external exposure when installing open-source tools, close unnecessary ports, patch network devices, and follow advisories for the affected products, including LiteLLM 1.83.7 or later and Ivanti Sentry R10.5.2, R10.6.2, or R10.7.1.
More hardware news from TechManNews.