The stories logged on this beat share one thread: data breaches increasingly arrive disguised as ordinary product and infrastructure changes. A Kindle leak, a Walmart pricing pledge, and an agentic Azure attack are not the same event, but each shows where personal and corporate data sits exposed. For US technology companies and consumers, the breach surface is widening from obvious hacks to routine updates, vague commitments, and automated cloud intrusions.
Leaks Are Breaches Too
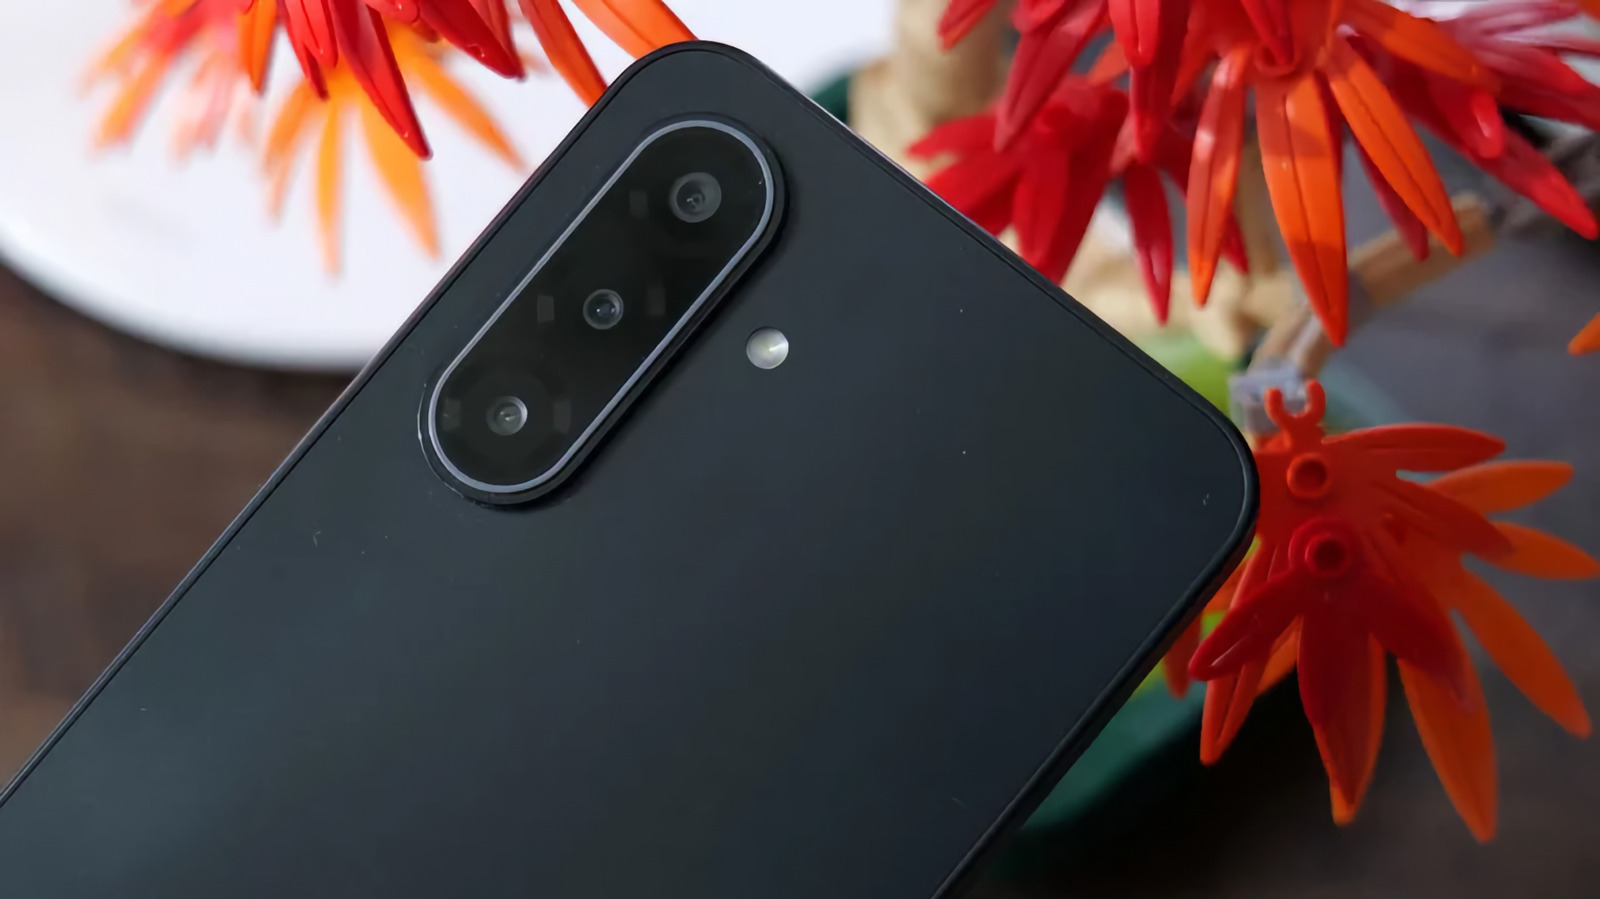
The Verge reported leaked images revealing new colors for Amazon's next entry-level Kindle, with the company typically introducing new models ahead of the holiday shopping season. On its face, this is a product story. On the Data Breaches beat, it is a reminder that unreleased hardware details circulate before launch, and that controlled information rarely stays controlled.
Amazon has not confirmed the colors, and the leak does not by itself expose customer records. But the pattern matters. Product pipelines, supplier communications, marketing assets, and retail partner systems all hold fragments of a launch. When an image surfaces early, it signals that someone outside the intended circle had access, or that a system holding that material was reachable. The Verge's report does not identify the source, which is typical.
For US consumers, the practical risk is not a leaked color swatch. It is that the same channels that move embargoed images can move customer data. A device launch involves preorders, account linkages, and support systems. Each is a potential breach point. The Kindle leak is a low-stakes example of a high-stakes habit: companies treat pre-launch confidentiality as a marketing problem, when on this beat it is an access-control problem.
Walmart's Pricing Pledge Is a Data Governance Statement
Walmart CEO John Furner wrote to customers that the company will not change product prices based on personal information or time of day, as reported earlier by The Wall Street Journal and covered by The Verge. The letter responds to concern that digital shelf labels would enable dynamic pricing. Furner said the switch is meant to save store associates time.
The denial is notable because it is a statement about data use, not just pricing. Walmart is telling customers that shopping history and personal information will not feed price changes. That is a commitment about how data flows inside a large retail operation. On the Data Breaches beat, such commitments are only as strong as the systems that enforce them.
Digital shelf labels are networked devices. They sit inside stores, connect to inventory and pricing systems, and depend on credentials and updates. A breach that reaches those systems could alter prices, disrupt operations, or expose data about how a store is run. Walmart's letter addresses the pricing question. It does not describe the security architecture behind the labels, and The Verge's report does not say it does.
For US consumers, the episode shows how quickly a convenience upgrade becomes a data question. Shoppers are being asked to trust that personal information will not be used in a new way. That trust depends on breach prevention, not just policy language. If a retailer cannot keep its shelf-label network and pricing systems separate from customer data, the pledge is a promise without a technical guarantee.