📣

Advertisement

Google Ad - 970×90 Leaderboard  TOP_LEADERBOARD_4

The Trusted Channel Is Now the Attack Surface
Article

The Trusted Channel Is Now the Attack Surface

Four recent incidents show attackers exploiting the infrastructure and identity checks that security teams already trust.

Arjun NairSeptember 17, 20265 min read

Photo: BleepingComputer

📣

Advertisement

Google Ad - 970×90 Leaderboard  TOP_LEADERBOARD_4

The common thread in this week's cybersecurity news is not a new malware family or a novel exploit technique. It is that attackers are increasingly operating through channels that victims have already decided to trust: a marketing platform's API key, a valid login, a camera vendor's own storage, a backdoor built to look like routine government traffic. Each story describes a compromise that succeeded because the defensive perimeter was drawn around the wrong thing.

Trusted Vendors as Launch Pads

The Brevo supply-chain attack, reported by BleepingComputer, is the clearest example. Attackers stole a Cloudflare API key and used it to inject ClickFix scripts into Brevo's websites and into JavaScript files embedded on customer sites. The victims here are not Brevo's own users in any direct sense. They are the visitors to customer websites that had loaded Brevo's code in good faith. A single stolen credential at a vendor became a malware delivery mechanism across an unknown number of downstream properties.

This is the supply-chain problem in its current form. The compromise does not require breaking into each customer. It requires breaking into one party that many customers have already granted embed rights. For US technology companies, the practical implication is that vendor risk is no longer just about data access. It is about code execution in the browser of every visitor to a customer's site. A marketing or analytics vendor with JavaScript on the page has, in effect, a permanent position inside the customer's perimeter. The Cloudflare API key in this case was the specific lever, but the structural weakness is the trust relationship itself.

Identity Verification Stops at the Wrong Point

The second BleepingComputer story, a Specops analysis of AI-powered attacks, makes a related argument from the defensive side. AI is making credential theft faster and easier to scale, giving attackers more opportunities to abuse valid identities. The piece argues that identity security must move beyond successful authentication and verify that both the user and the device requesting access can be trusted.

The pairing with the Brevo incident is instructive. In one case a stolen API key granted access to a vendor's systems. In the other, the concern is stolen credentials granting access to enterprise systems. Both describe authentication that succeeded while the underlying request was malicious. The industry has spent years improving login security, and that work has value. But the Specops argument is that login success is a weak signal when the credential itself has been stolen and the device is not what it claims to be. US enterprises buying identity tools should ask whether a product verifies the device and the behavioral context, or simply checks the password and the second factor.

Espionage Quietly Modernizes

The FamousSparrow story from BleepingComputer adds a different dimension. The China-linked group has been using a new backdoor named SparroWocky against government organizations in Latin America. The target set and geography are specific, but the pattern is not. An established espionage actor has refreshed its tooling with a new backdoor, which is the normal maintenance cycle of a persistent threat group.

The relevance to US technology companies is indirect but real. Backdoors used in regional espionage campaigns tend to spread, get repurposed, or inform the tooling of other actors. A new implant deployed against government targets in one region is a signal about capability, not just about that region. For defenders in US government-adjacent sectors, the takeaway is that the tooling pipeline has not stood still even when the headlines have focused elsewhere.

Advertisement

📣

728x90

MID_CONTENT_2

The Camera That Kept More Than It Should

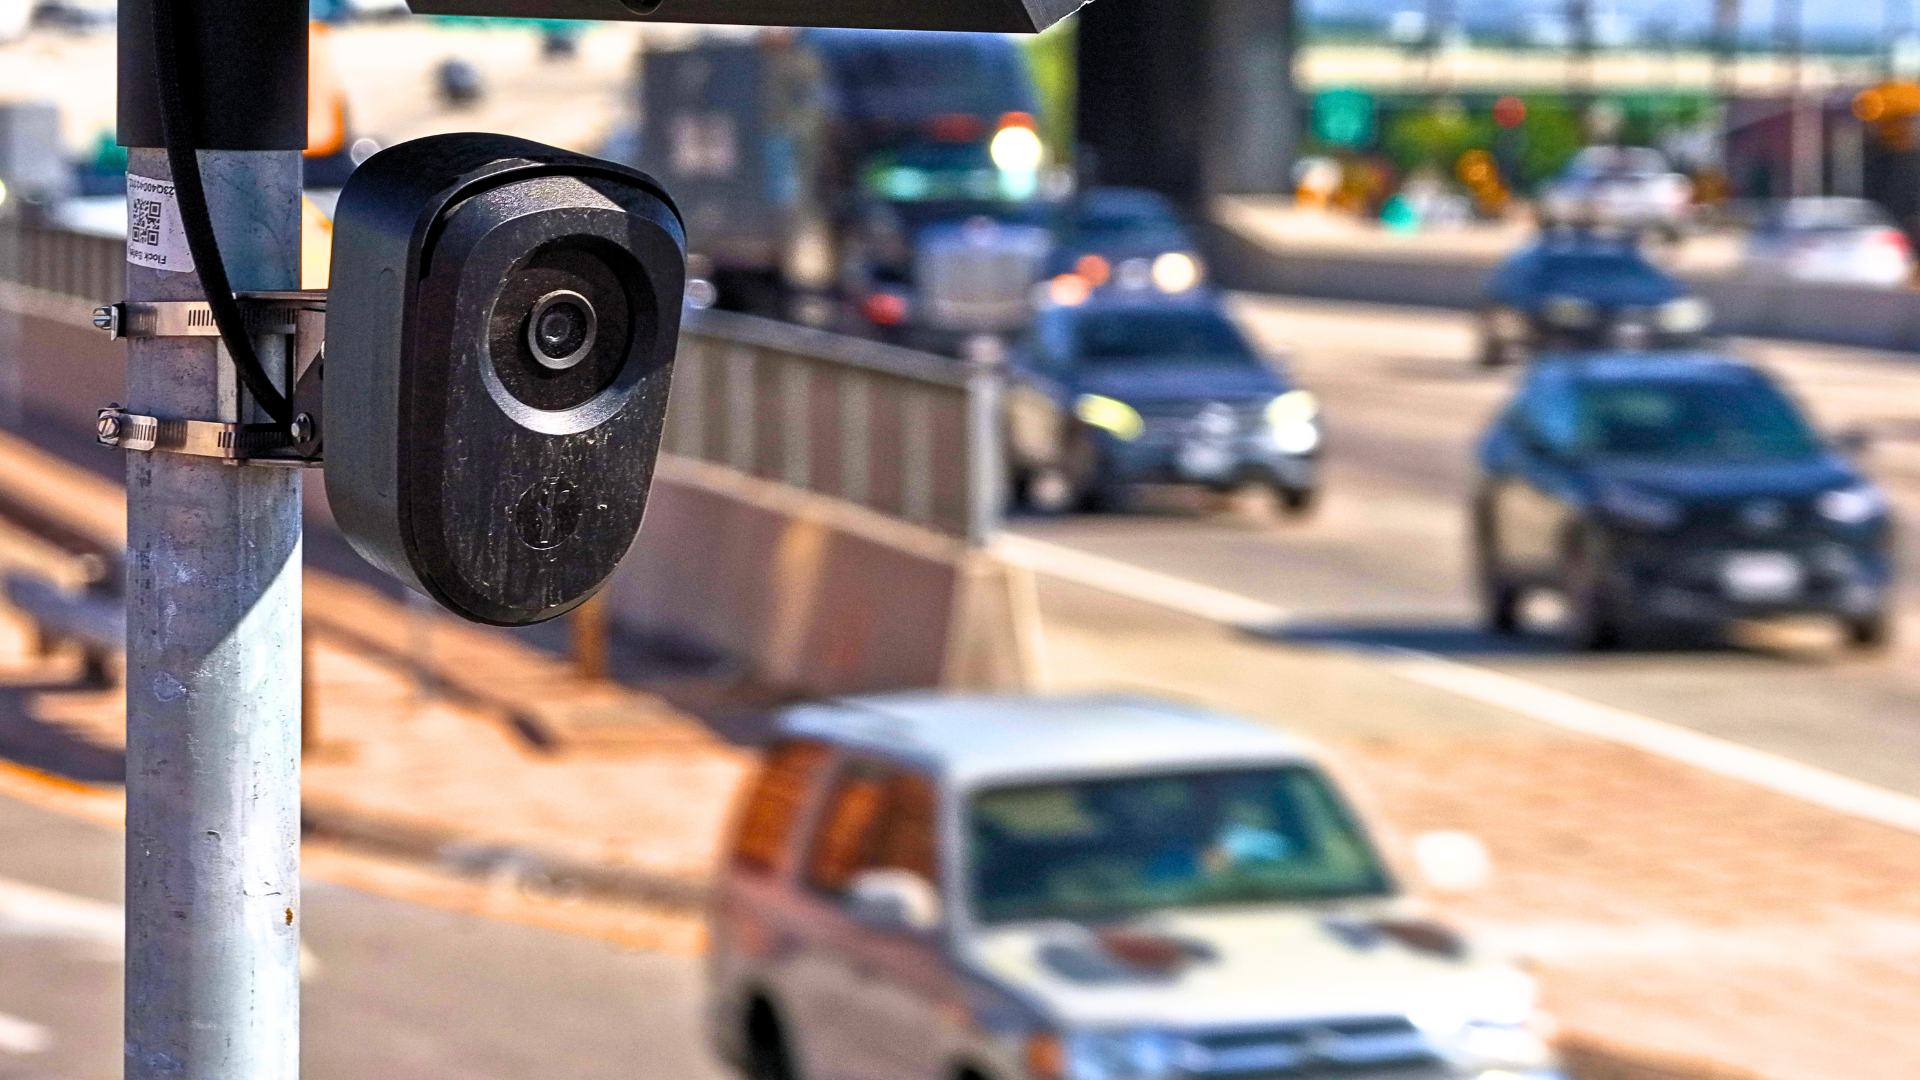
Tom's Hardware reported that the hacking group stegan0gram obtained a Flock camera and broke into its systems, extracting more than 27,000 clips and 1.6 million images captured over 21 days, despite the company's denials about stored encryption keys. The group also found the device could detect people, not just cars, motorbikes, and license plates.

Two things stand out. First, the volume of retained data is large for a device whose public framing is about vehicle identification. Second, the encryption keys were reportedly stored on the device itself, which is what made the extraction possible. A physical device deployed in public space is, by definition, reachable. If it stores its own keys and retains weeks of footage and imagery, then compromise of one unit yields a substantial intelligence haul. The detection of people rather than only vehicles expands what that haul contains.

For US consumers and municipalities, this matters because camera networks have been expanding on the promise of narrow, specific function. The reported capability set and the reported data retention suggest the actual footprint is broader. Buyers evaluating these systems should ask where keys are stored, what is retained, and for how long, rather than accepting the stated use case.

Why These Four Belong Together

Each story describes an attack that worked because a control was trusted past the point where trust was warranted. The vendor's API key. The successful login. The espionage group's assumed toolset. The camera's own key storage. In every case, the defensive assumption was that the trusted element would remain trustworthy, and in every case that assumption failed.

The unifying lesson is that the modern attack surface is largely composed of the things organizations have already decided not to question: embedded third-party scripts, authenticated sessions, established threat actors, and deployed hardware. None of these are new categories. What is new is the consistency with which they are being used as the entry point rather than the target. US technology companies that map their exposure by asking "what have we granted trust to, and how would we know if that trust were abused?" will be asking the more useful question than those still drawing the perimeter around their own network edge.

What to Watch

The stories above point to a few concrete things worth tracking. Whether Brevo discloses how many customer sites were affected by the injected ClickFix scripts, and whether Cloudflare API keys become a named item in vendor security questionnaires. Whether identity vendors follow the Specops argument and ship device-and-user verification as a default rather than an add-on. Whether SparroWocky samples surface in analyses of attacks outside Latin America, which would indicate the tooling has spread. And whether Flock responds to the stegan0gram findings with specifics about key storage and data retention, or with another denial.

None of these are predictions. They are the open questions the reporting leaves behind, and they are the ones that will determine whether the pattern described here holds or breaks.

More on this beat: Cybersecurity on TechManNews.

Advertisement

📣

728x90

IN_ARTICLE_5

#supply chain#identity security#espionage#surveillance#vendor risk#cybersecurity

Newsletter

Get Tech News in Your Inbox

The latest AI, gadgets, software and startup stories from TechManNews, delivered every morning - free.