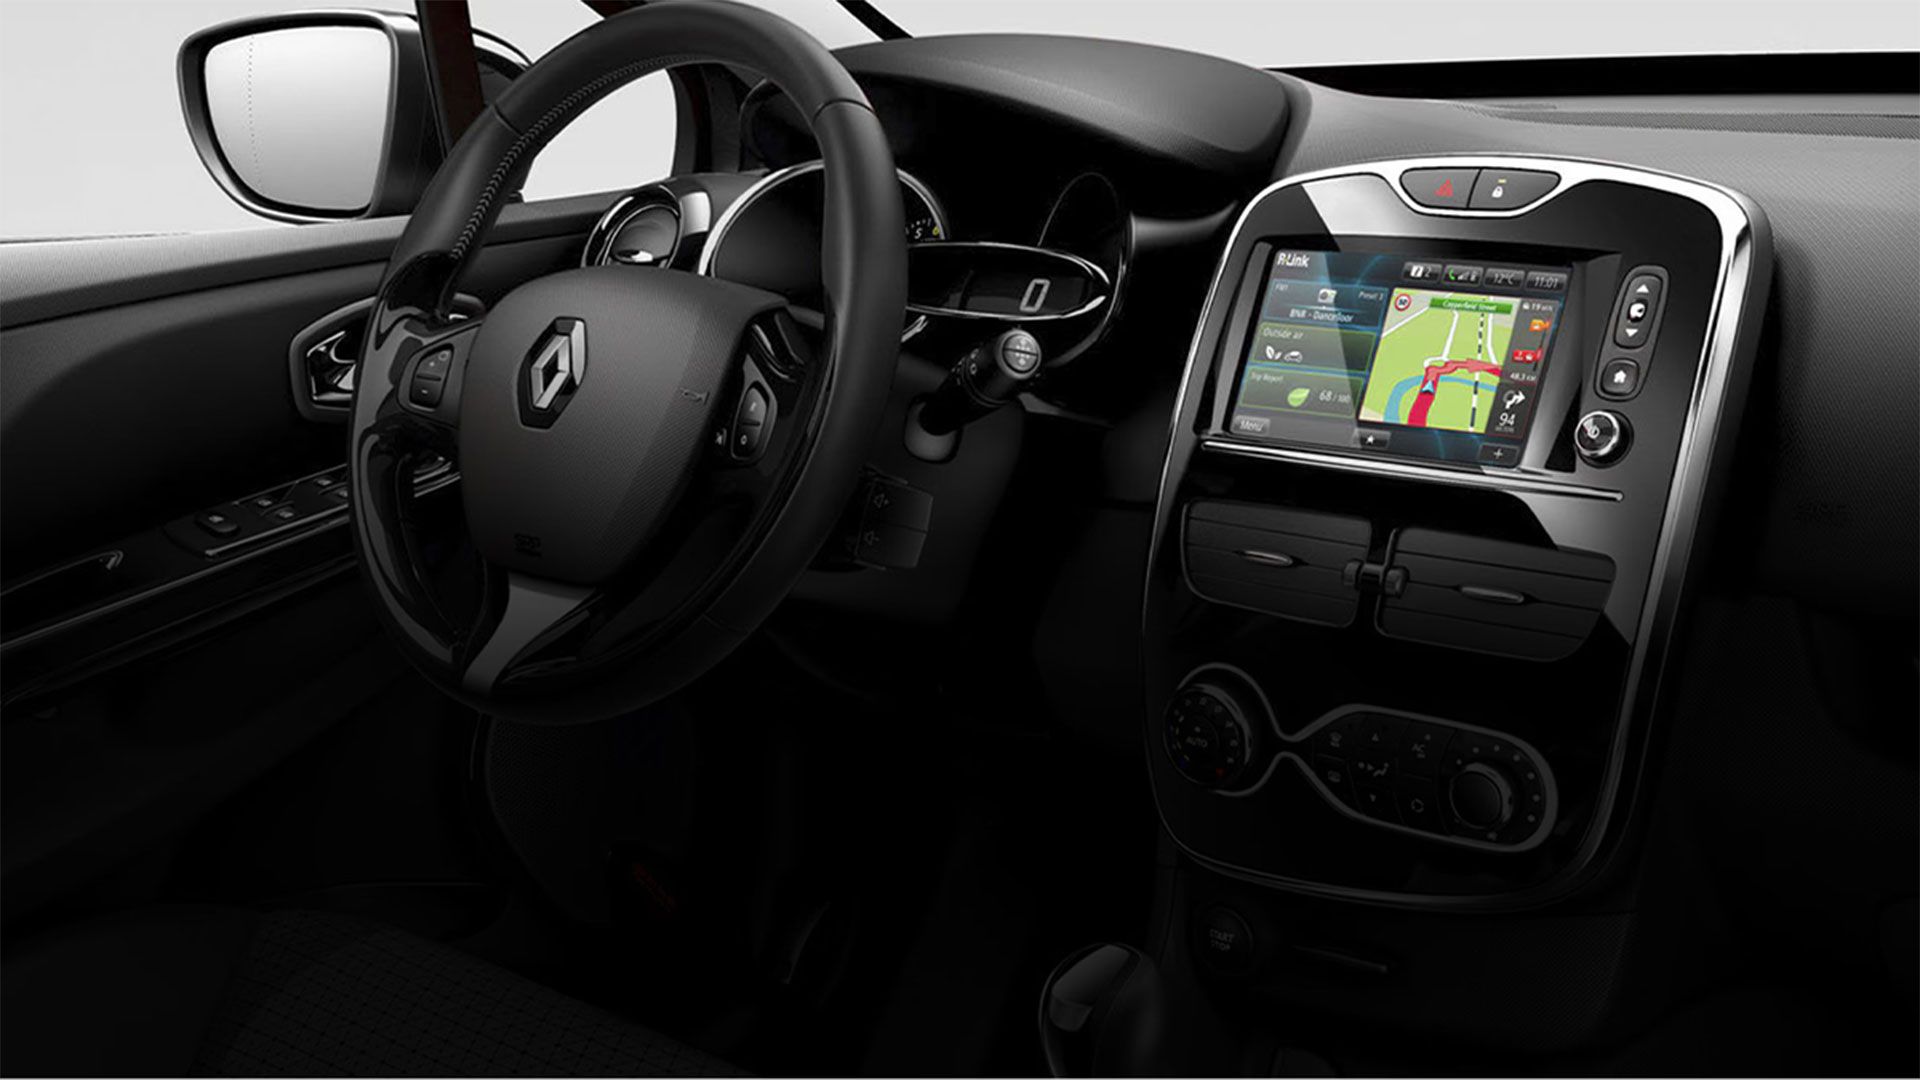
A security researcher who bought a used 2014 Renault Latitude found that adjusting the in-car clock required jailbreaking the vehicle's infotainment system. The researcher, Moorats, had been told by the previous owner that an SD card was needed to change the time on the display, but doubted the claim and left the card out because the maps it carried were chronically out of date.
The problem surfaced when daylight saving time arrived and the dash clock sat an hour off. The in-dash system offered two settings menus; one covered Bluetooth and Phonebook options and was of no use for the clock. The second menu refused to open any submenu, showing a "No maps detected!" error each time it was selected.
Moorats, drawing on his security background, reverse engineered the unit. He found it ran a customized Linux-based TomTom operating system on a Samsung SoC. He extracted and analyzed the firmware, built a QEMU environment for the device, reversed the scripting engine, and uncovered a number of vulnerabilities in the system.
The successful entry came from an approach borrowed from kernel exploit techniques he uses in his day job. Rather than trying to get the userland to run his script, he had the kernel execute it instead, which gave him root-level access to the infotainment system.
Once inside, Moorats located the date and time settings in /mnt/flash/settings.dat, stored in a custom binary format. He observed in his blog post that the system has no real concept of time zones: it takes the time from GPS and stores the local offset as a number of minutes. His was set to 180, and he changed it to 120.
The episode highlights how deeply embedded infotainment software can gate basic functions behind map data, leaving owners of the 2014 Renault Latitude unable to perform a routine clock adjustment without exploiting the head unit. For US drivers, the case is a reminder that connected and non-connected vehicle systems alike can tie simple cabin settings to components owners may not have or may not want.
Moorats' findings, including the vulnerabilities he uncovered during the work, were detailed in his blog post on the project.
More hardware news from TechManNews.