The recent hardware news points to a split in how physical technology is being made and used. Mainstream devices are becoming harder to service and less rewarding to tune, while the most ambitious tinkering is moving to small, self-directed projects. For US companies and consumers, that means the practical life of everyday hardware and the culture of hardware enthusiasm are pulling in different directions.
Repairability Is Now a Design Choice
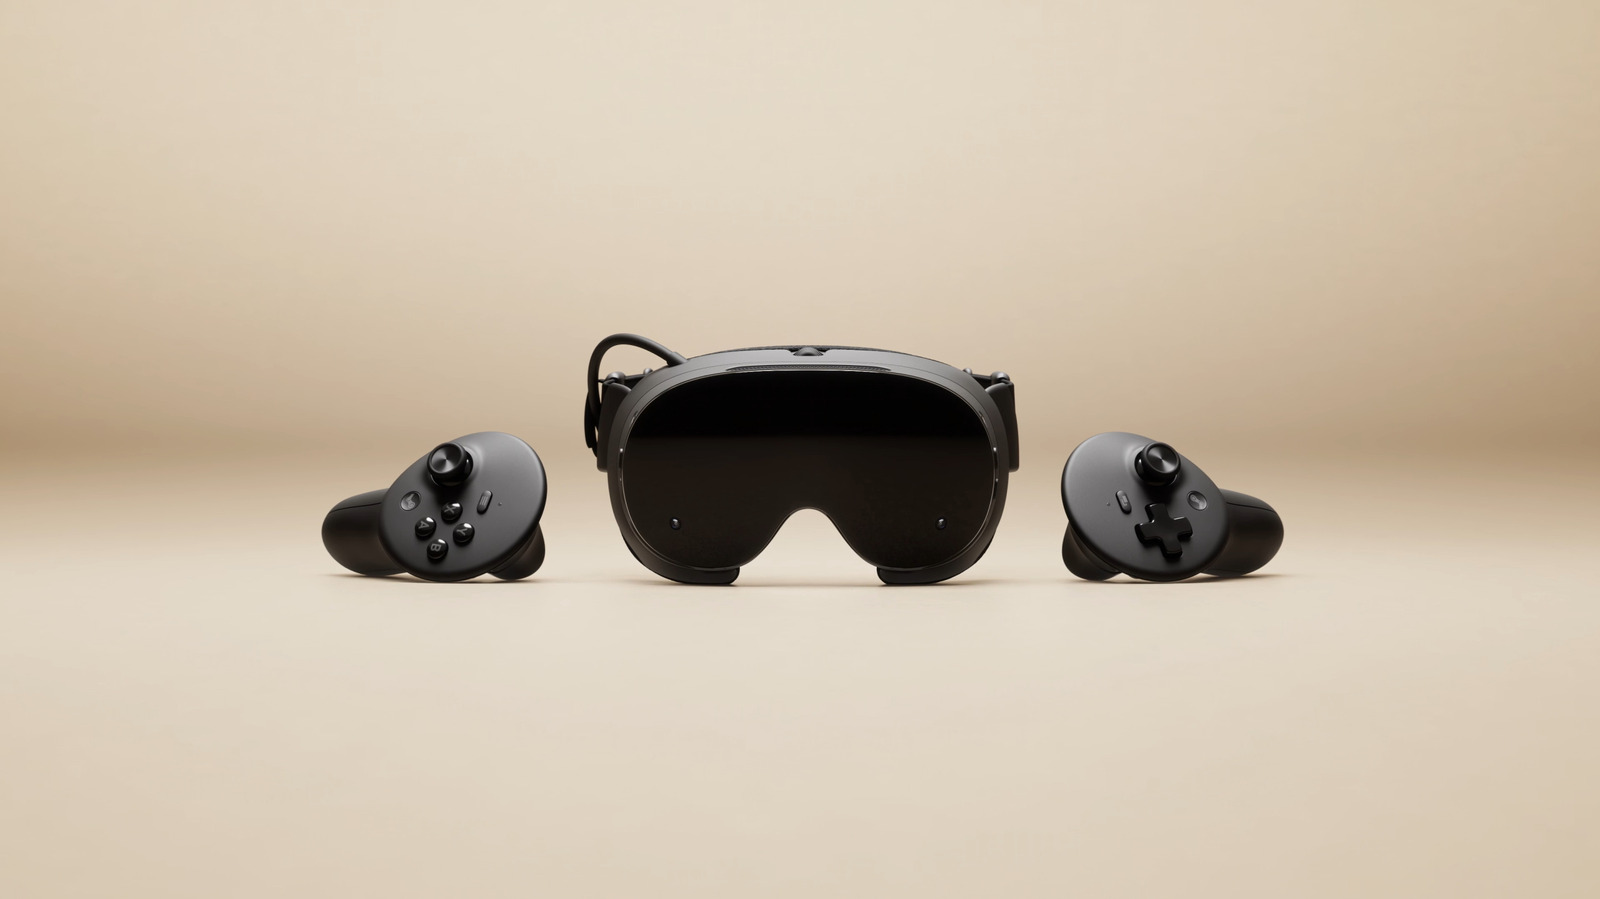
Engadget's teardown of the Steam Frame found an otherwise repairable device with one significant exception: the cooling fan is hard to reach. The detail matters because it shows repairability is not a single feature that a product either has or lacks. It is a set of decisions made component by component, and a single difficult part can undercut the value of an otherwise open design. A fan is also a wear item. It is one of the parts most likely to fail or accumulate dust over a device's life, so burying it raises the cost and difficulty of the repair most likely to be needed.
For US consumers, that translates directly into ownership cost and downtime. A device that can be opened, but not easily kept cool, still pushes owners toward professional service or replacement. For US companies, it complicates the repairability claims that have become a selling point in some product categories. A teardown that praises most of the design and flags one inaccessible component is a reminder that partial repairability can be a marketing position as much as an engineering outcome.
The Limits of Tuning Mainstream Silicon
Engadget also reports that CPU overclocking is mostly now a thing of the past, because the performance gains available from modern chips are not as noteworthy as they once were. That is a change in the relationship between users and their hardware. Overclocking was once a way for enthusiasts to extract meaningful extra performance from a processor, and it sustained a whole culture of motherboards, cooling, and community benchmarking. If the gains are no longer significant, the incentive to learn and invest in that practice weakens.
The effect on the US market is a further shift of control toward manufacturers. When tuning yields little, buyers rely more on the performance tiers the vendor decides to sell, and the practical differentiation between adjacent products narrows. Enthusiast energy that once went into tuning mainstream parts has to go somewhere else, and the remaining stories suggest where.
When the Threat Is in the Tooling
Tom's Hardware reports that Lumen's Black Lotus Labs says a cryptomining malware family called PoeLLM has hit more than 3,400 servers, most of them exposed AI tools such as LiteLLM and Ollama, and that it locates its control server in a GitHub poem. Two things stand out. The first is the target: not general-purpose servers, but the AI tooling that has been deployed quickly and often left exposed. The second is the technique. Hiding command-and-control instructions in a poem on a public code-hosting site is a way to blend malicious traffic into a service that many networks already trust and allow.
The count of more than 3,400 servers is a reminder that the rapid adoption of AI infrastructure has expanded the attack surface faster than it has been secured. For US companies running internal or customer-facing AI tools, the practical lesson is that an exposed inference or orchestration service is a compute asset, and compute assets are worth stealing. For US consumers, the downstream cost is less visible but real: abused servers consume power and bandwidth, and the organizations running them absorb incident response and remediation costs.