Breach Beats Are Learning the Wrong Lessons From Clean Wins

Photo: BleepingComputer

Article

Breach Beats Are Learning the Wrong Lessons From Clean Wins

ManishankarOctober 14, 20264 min read

Three recent security-adjacent stories show that narrow victories and untested surfaces are becoming the dominant risk pattern in US breach defense.

The stories crossing the data breach beat this week share one uncomfortable pattern: the wins are narrower than they look, and the surfaces that remain untested are where breach risk accumulates. A court verdict that costs a defendant almost nothing, a security tool that cannot reach most of the estate, and a major product launch that deliberately withholds a platform are all signals that visibility and accountability are being optimized down to the minimum. For US companies and consumers, that means the breach surface is not shrinking even as headlines suggest progress.

The Agentic Pentesting Gap BleepingComputer Flagged

BleepingComputer reports on Picus Security's account of agentic penetration testing, and the finding is blunt: AI-powered testing can trace complex attack paths, but safety restrictions and network limitations leave many assets and vulnerabilities untested. That is not a minor caveat. It is a structural gap in how US enterprises are currently validating their defenses.

The breach implication is direct. If a testing tool cannot reach an asset, the pre-breach assurance work skips that asset. An attacker does not. US companies that have shifted budget toward automated offensive testing may believe they have coverage that does not exist. Picus's suggested answer, per BleepingComputer, is to combine agentic pentesting with exposure validation and breach simulation, which is an admission that no single method closes the loop.

For American security teams, this is the same coverage illusion that has driven so many breach post-mortems: the tools report on what they can see, and the board reads the report as a measure of the whole estate. The gap between tested and untested assets is exactly where breach dwell time grows.

Why a Two-Dollar Verdict Is a Breach Risk Signal

Engadget reports that Qualcomm won its lawsuit against Arm, with a jury finding that Arm breached its agreement with Qualcomm and interfered with its business, but Arm only has to pay two dollars in damages. On its face this is a licensing story. On the breach beat, it matters because legal accountability is one of the few forces that can move security investment.

A two-dollar damages award tells every technology company watching that contract and supply-chain breaches can be adjudicated as wins for the plaintiff while imposing essentially no financial consequence on the defendant. The deterrence value is near zero. For US companies that depend on licensed IP and third-party silicon, that is a problem: the legal system is unlikely to force better security behavior in commercial relationships, so the burden falls back on the buyer's own breach controls.

This connects to a broader pattern in US breach response. When liability is small, remediation is optional. Companies make risk decisions on expected cost, and expected cost just got cheaper for the losing side.

The Platform Left Off the Launch Is the Unmonitored Asset

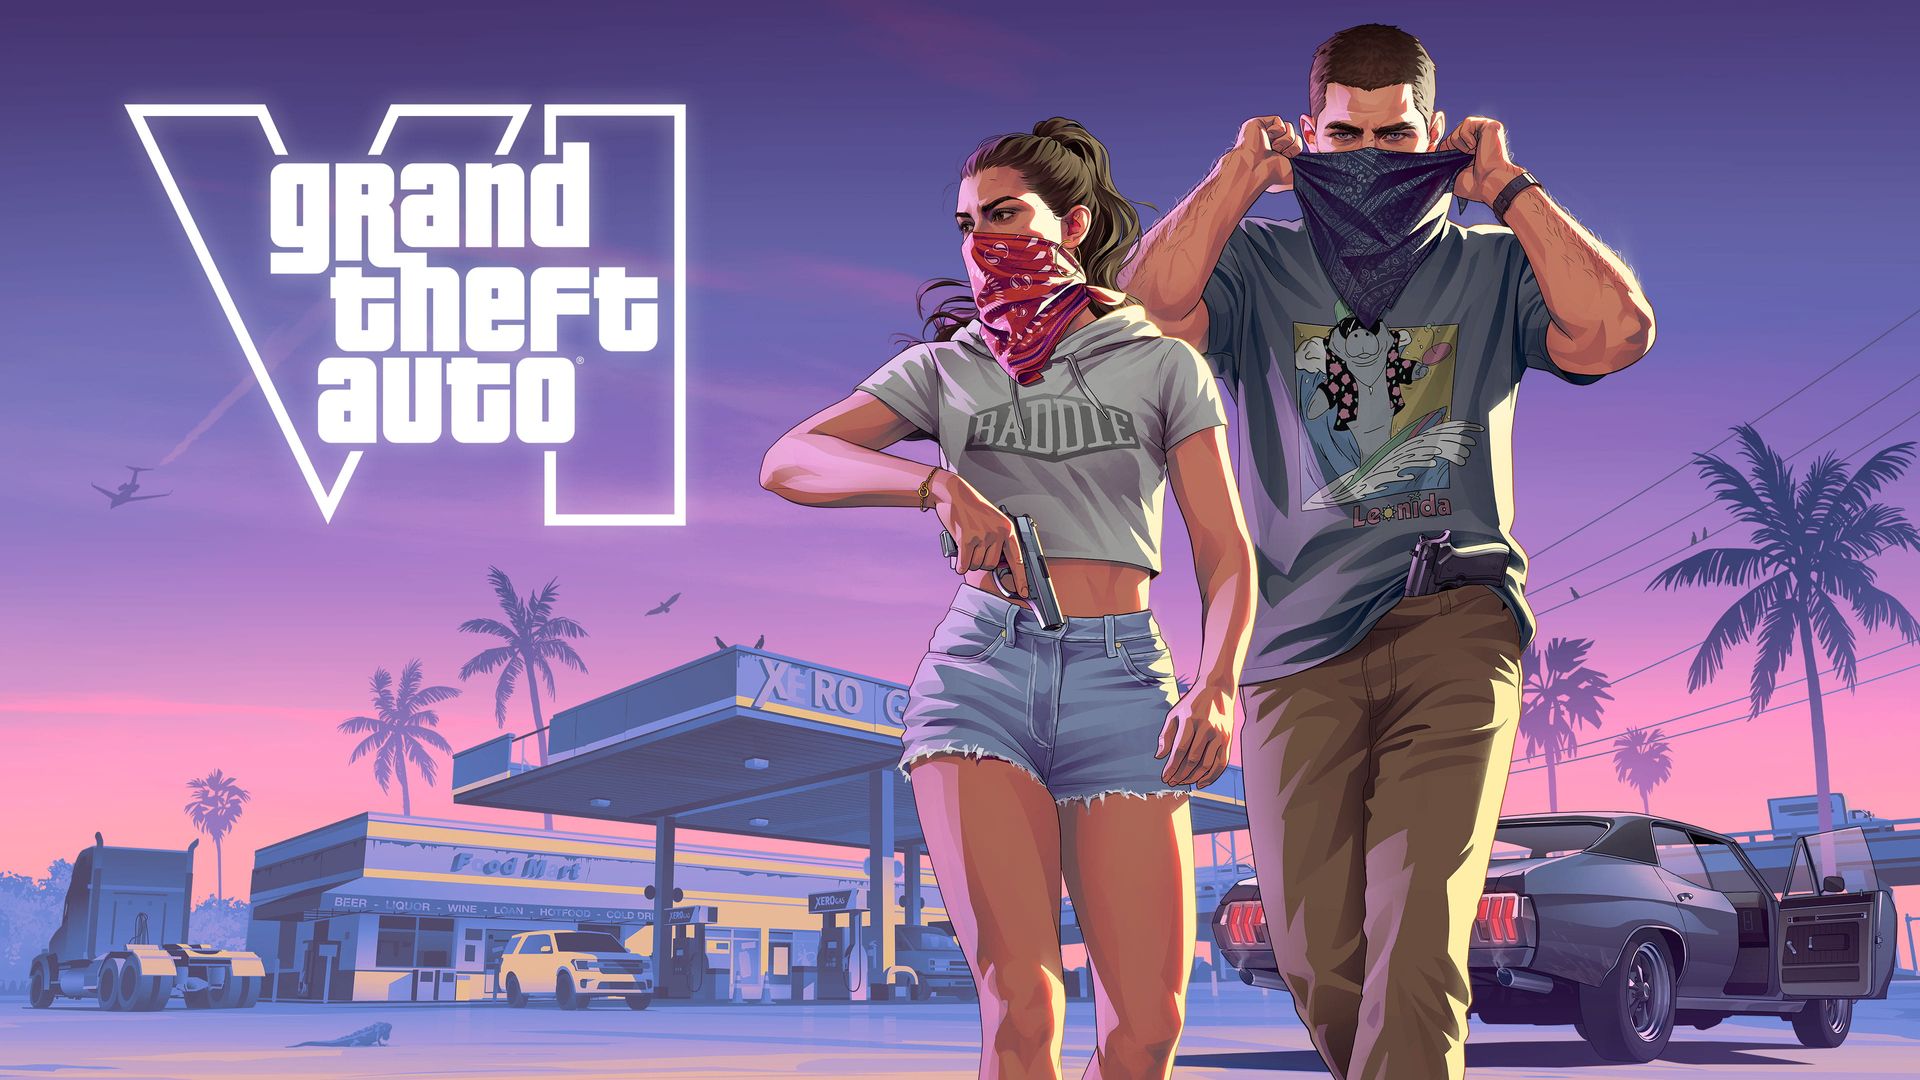
Tom's Hardware reports that GTA 6 will be console-only at launch, with a PC launch now expected within the first three months of 2027. This is not a breach story on its face. It becomes one when the same logic that leaves a platform off a launch calendar also leaves it off a security calendar.
US consumers and enterprises plan around launch windows. A PC release that arrives months after the console version creates a second, less-prepared wave of installs, mods, and account activity. Historically, that wave is where credential stuffing, account takeover, and malicious tooling cluster, because the audience is large, the platform is open, and the security posture was designed for a different timeline.

The breach implication is not about the game itself. It is about the pattern: when a major product defers a platform, security teams that support that platform inherit a compressed preparation window. In the US market, where PC gaming and PC-based enterprise environments overlap heavily, that compression lands on the same identity and endpoint systems that breach actors already target.

The Connecting Thread: Wins That Do Not Reduce Exposure

All three stories describe outcomes that look favorable and reduce exposure less than they appear to. A pentesting advance that cannot reach many assets, a legal win that costs the defendant two dollars, and a launch that keeps a platform off the schedule until 2027 all share the same shape: the headline improves, the breach surface does not.

For US technology companies, this is the central risk management problem of the current cycle. Security spending is justified by activity and by favorable outcomes, not by coverage. The Picus framing that BleepingComputer relayed, exposure validation plus breach simulation, is an attempt to measure coverage rather than activity. The Qualcomm verdict undercuts the legal pressure that would otherwise force coverage. The GTA 6 timeline shows how coverage is planned around the loudest platform, not the most exposed one.

US consumers feel this in the same way. Their accounts, credentials, and devices live on the platforms and vendors that these stories describe as low-priority or under-tested. When a PC version arrives in early 2027 without a security budget built for it, the breach that follows is not a surprise. It is a scheduling outcome.

What the Breach Beat Should Watch

The measurable items in these stories are the ones worth tracking. BleepingComputer's account gives US security teams a concrete question to ask vendors: which assets does your agentic tooling actually reach, and which are excluded by safety restrictions or network limits. Engadget's report on the two-dollar verdict gives boards a concrete question about supplier contracts and enforcement. Tom's Hardware's report gives platform and identity teams a concrete timeline: the expected PC window in the first three months of 2027.

None of these are breach incidents yet. That is the point. The breach beat in the US is increasingly written by the gaps that appear before an incident, in testing coverage, in liability, and in launch schedules. The stories above are the gaps, documented in plain sight.

Sources: BleepingComputer, Tom's Hardware, Engadget.

More on this beat: Cybersecurity on TechManNews.

#data breaches#cybersecurity#agentic pentesting#exposure validation#US technology#breach risk

Newsletter

Get Tech News in Your Inbox

The latest AI, gadgets, software and startup stories from TechManNews, delivered every morning - free.