The pattern running through these stories is that data breaches keep being produced by the oldest and least glamorous layer of the stack. An incident at 700 supermarkets, traced to outdated devices left exposed to the Internet, shows that the failure was not exotic: it was ordinary neglect sustained over years. Meanwhile, the conversation about AI-powered pentesting is about coverage gaps, and even a games-industry leak story turns on how a product reaches the public rather than how it is protected. The thefts may be quiet, but the means are stable: forgotten devices, untested assets, and information that leaks before anyone secures it.
The Fridge Incident Is the Whole Lesson
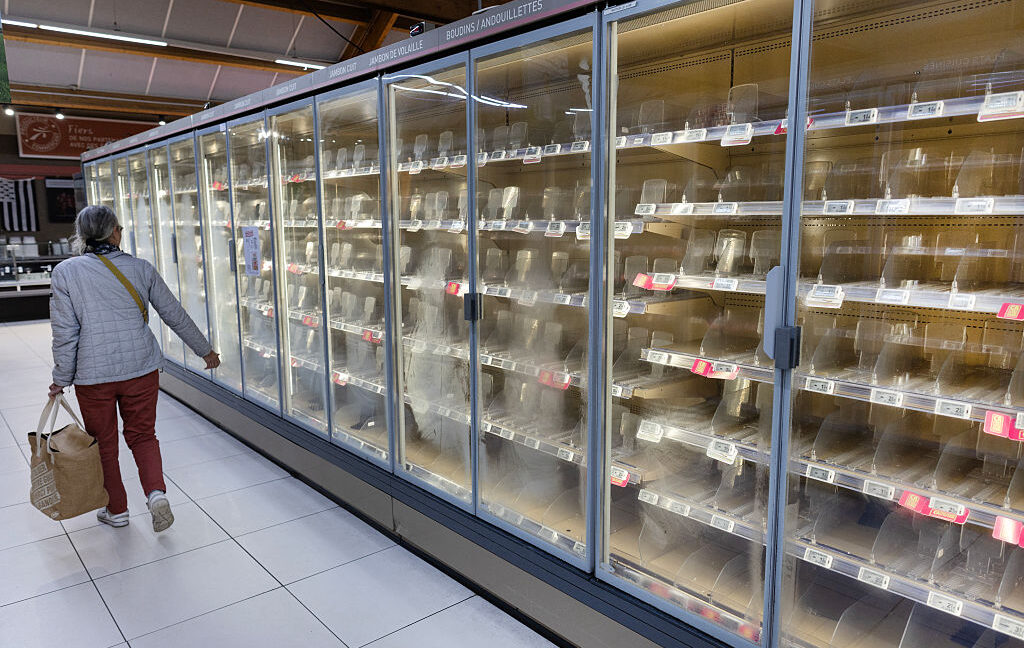
Ars Technica reports that the incident hitting 700 supermarkets exploited outdated devices exposed to the Internet. The consequences were not confined to data. The hack cost millions and sparked fires, which is the part US companies should read twice. A breach that starts with a device nobody administered ended in physical damage and a seven-figure bill.
The failure was not a sophisticated adversary outrunning a modern defense. It was a device that should have been retired or isolated, sitting on the open Internet. For US retailers, grocery chains, and the distributed operators that dominate the sector, that description fits a large share of store-level infrastructure. Point-of-sale peripherals, refrigeration controllers, environmental sensors and building-management systems are frequently installed by contractors, left running for a decade, and never brought under the same inventory, patching and monitoring regime as corporate IT.
What makes this case a landmark is the scope. Seven hundred sites means a single class of weak device became a fleet-wide exposure. The cost figure and the fires are outlets' characterisation of the damage; the underlying mechanism is the one US security teams already know. The perimeters that hurt most are the ones nobody owns.
The Uncovered Assets Behind Agentic Pentesting
BleepingComputer carried Picus Security's account of the blind spots of agentic pentesting. The argument there is not that AI-driven testing fails. It is that safety restrictions and network limitations leave many assets and vulnerabilities untested, and that combining agentic pentesting with exposure validation and breach simulation can close those gaps.
That is the same story as the fridges, told from the defender's side. AI-powered testing can map complex attack paths, but the assets outside its reach are often precisely the legacy, segmented or awkwardly networked devices where breaches begin. Validation and simulation are proposed as the remedy, which concedes an important point: discovering a flaw is not the same as proving it is exploitable in the environment where it lives.
The US implication is budgetary and organisational. Enterprise security spending has moved toward automated tooling, and agentic pentesting is being sold as a coverage multiplier. If the coverage stops at the edge of the network segment, the retailer still has a fridge problem. Buyers should be asking vendors not how many paths the tool found, but which assets it could not see.